
AI Transformation With Human Oversight, From First Use Case to Everyday Operations
AI transformation for regulated organisations: choose the right first use cases, prepare the data behind them and bring AI into everyday operations, with people approving every output that affects someone and a log behind every action.
The board wants an AI plan, the risk committee wants evidence, and staff are already pasting documents into public chatbots. Thornacre’s AI transformation service takes you from choosing the first use cases to running AI in everyday operations, with people approving every output that affects someone and a log behind every action.
| At a glance | Detail |
|---|---|
| Who it is for | CTOs and IT Directors, Heads of Data, CISOs, DPOs and Compliance Leads, and COOs in any regulated organisation |
| The problem it solves | AI ideas with no priority, data not ready for AI, shadow AI use, and pilots that stall at risk review |
| What we deliver | A ranked use case portfolio, data readiness checks, an AI policy and controls, measured pilots, and AI in live operations with human checkpoints and logs |
| How we work | Agile delivery as the GDS Service Manual describes, with controls from the AI Playbook for the UK Government and ICO guidance |
| Regulations and standards | UK GDPR, ICO guidance on AI, AI Cyber Security Code of Practice, EU AI Act |
What problem does AI transformation solve in regulated organisations?
AI transformation turns scattered AI ideas and unapproved tools into governed AI in everyday operations, without risk the organisation cannot explain to a regulator.
AI transformation is the planned adoption of AI across an organisation: ranking use cases, readying their data, setting controls and scaling what works. Use cases fall into five families:
- Assistants and copilots: staff search, summarise and draft inside approved tools.
- Document and data extraction: fields read from forms and letters into the line-of-business system.
- Classification and triage: requests sorted and routed to the right team.
- Forecasting: demand, workload or risk predicted from historical data.
- Workflow automation and agents: an AI agent is a model that carries out several steps across systems, with a human checkpoint before anything takes effect.
The Office for National Statistics (ONS) found that the share of UK businesses with 10 or more employees using at least one AI technology rose from around 12% in late 2023 to around 35%, and to 49% among those with 250 or more employees.
Each persona feels a different part of the problem:
- COO or Operations Director: queues of work that skilled staff read, rekey and route by hand.
- CTO or IT Director: AI tools bought team by team, none connected to core systems.
- Head of Data: AI ideas stalled on data that is siloed or has no lineage.
- CISO: customer and staff data flowing into public AI tools nobody approved.
- DPO or Compliance Lead: pilots that cannot show how an output was produced or who checked it.
None of this is anyone’s fault. Core systems were bought to store records, not read them, and AI tools are sold one product at a time when the risk sits in how each output is used.
How does Thornacre deliver AI transformation with human review?
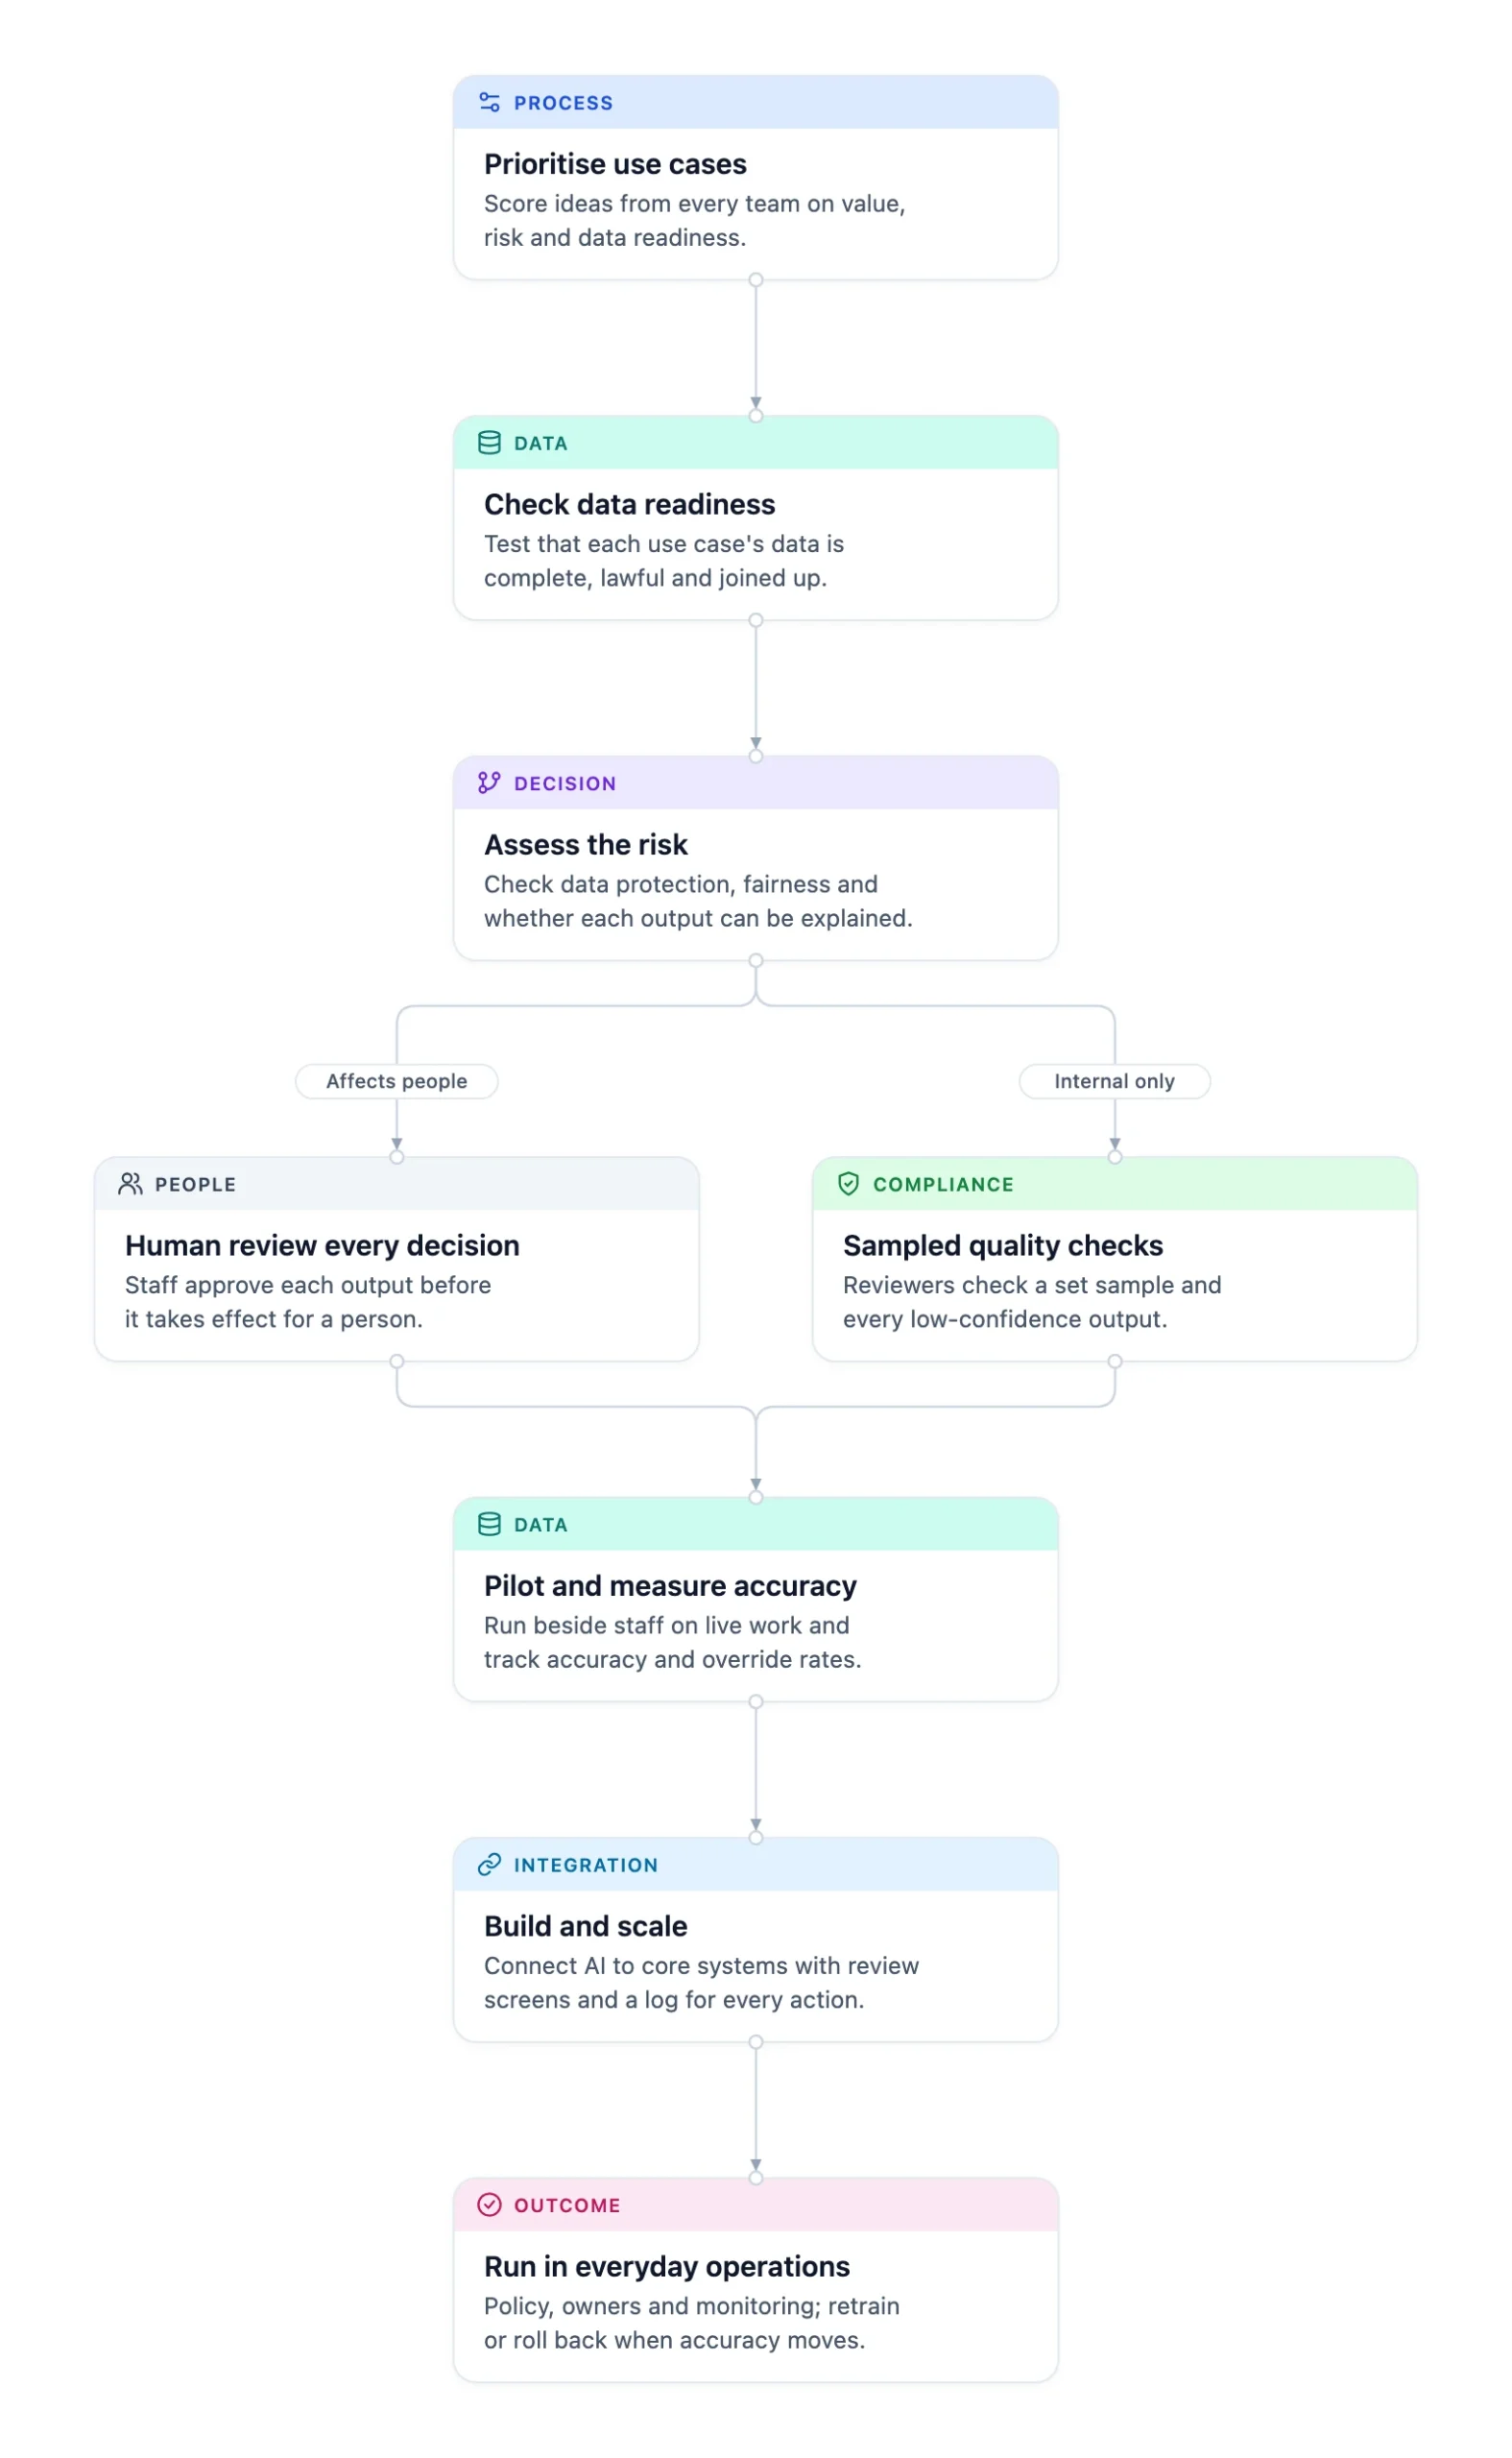
Thornacre delivers AI transformation in six phases, from ranking use cases to running AI in everyday operations. Delivery is agile, as the GDS Service Manual describes, and the controls follow the AI Playbook for the UK Government.
- Prioritise use cases. Score ideas from every team on value, volume, risk and data readiness. Outcome: a ranked portfolio of quick wins and larger automations.
- Check data readiness. Test whether each use case’s data is complete, reachable, lawful to use and joined up. Outcome: a go-ahead or a fix list per use case.
- Assess the risk of each step. Test data protection, fairness, security and explainability. Does the output affect a person? If yes, staff approve every output. If internal only, reviewers check a sample and every low-confidence case. Outcome: controls per step and input for your data protection impact assessment (DPIA).
- Pilot and measure accuracy. Run the AI beside staff on live work without acting on its output. Outcome: an accuracy figure per step, agreed before go-live.
- Build and scale. Connect the AI to your core systems, with review screens showing the source behind each suggestion, and extend to more teams once pilot figures hold. Outcome: every action logged with input, output and approver.
- Run in everyday operations. Set the AI policy, approved tools and an owner per use case, then track accuracy, overrides and drift; retrain or roll back when they move. Outcome: a regular report your DPO and process owner both sign.
The diagram shows the six phases and the fork at phase 3.
The unit of AI risk is the process step, not the project. One model can be safe for sorting post and unsafe for refusing an application.
Override rate is the figure to watch: a rate near zero may mean reviewers have stopped reading.
What do you get from an AI transformation engagement?
An AI transformation engagement leaves you working AI, the evidence to defend it and staff to run it.
| Deliverable | What you keep |
|---|---|
| Use case portfolio | Every idea scored on value, risk and data readiness, with data fixes listed |
| AI policy and controls | Approved tools, owners, review levels and per-step risk findings |
| Pilot report | Accuracy and override rates, measured on your own work |
| AI in operations | Assistants, extraction, classification, forecasting or agents in your systems |
| Review screens and logs | The source behind each suggestion, an approval step and a log entry |
| Handover | Accuracy reports, training and documents |
If source data needs work first, see data analytics and AI. For new connectors into core systems, see CRM and ERP integration and custom software development.
Which regulations does AI transformation help you meet?
AI transformation helps you meet UK GDPR, ICO guidance on fairness and accuracy, AI security principles and, for EU operations, the EU AI Act.
| Cross-sector standard | What it requires | How the service addresses it |
|---|---|---|
| UK GDPR Article 22C and ICO automated decision-making guidance | Safeguards for significant, solely automated decisions, including human intervention | Human review wherever a person is affected |
| ICO guidance on AI and data protection | Fairness, statistical accuracy, transparency and DPIAs | Per-step risk assessment and measured accuracy |
| AI Cyber Security Code of Practice | Baseline security principles for AI | Secure design to the Code’s principles with our cyber security team |
| EU AI Act | High-risk uses need human oversight and activity logging | Oversight and logging from the pilot |
Each sector adds its own rules, one example each:
| Sector | Regulation or framework | What it requires | How the service addresses it |
|---|---|---|---|
| Banking and payments | PRA SS2/21 | Management of outsourcing and third-party risk | Vendor AI models assessed as third parties |
| Insurance | FCA Consumer Duty | Evidence of good outcomes for retail customers | Overrides and complaints monitored by customer outcome |
| Private healthcare | UK GDPR Article 9 and the DSPT | Conditions for special category data; NHS data security standards | Data minimised per step and DPIA input |
| Life sciences | MHRA GxP data integrity guidance | Complete, attributable records with audit trails | Every AI action logged with its approver |
| Legal and professional services | SRA Standards and Regulations | Client affairs kept confidential | No client data sent to public AI tools |
| Public sector | Algorithmic Transparency Recording Standard | A published record of algorithmic tools in use | Use case portfolio and logs supply the record |
The AI Playbook for the UK Government sets 10 principles. This service follows Principle 4:
“You have meaningful human control at the right stages.” (GOV.UK)
How do you choose between an AI product and a built AI solution?
Choose an AI product, such as a licensed copilot, for generic tasks inside one system. Build when steps cross systems or the output affects a person.
| Criterion | Off-the-shelf AI product | Built AI solution |
|---|---|---|
| Speed to first result | Fast | Slower; a pilot comes first |
| Human review design | Whatever the vendor offers | Review screens and checkpoints designed per step |
| Logs for a regulator or auditor | Depends on the vendor | Every action logged in your systems |
| Third-party risk | Data processed in the vendor’s service | You control where data goes |
| Lock-in | High | Low; you own the workflow and logs |
Apply these rules:
- If a licensed assistant covers the task, approve it under the AI policy and spend build effort elsewhere.
- If the output routes, prioritises or refuses a person’s request, build human review into the workflow.
- If the process still runs on paper, digitise it first with digital transformation.
When is AI transformation not the right choice?
AI transformation is the wrong choice when volumes are low, rules are simple, or the decision should stay fully human.
- Low volume: a few hundred items a year rarely justifies a pilot.
- Simple fixed rules: if a decision table covers every case, rules-based workflow is simpler to run and easier to explain.
- Fully automated decisions about people: Thornacre does not build AI that decides about a person without a human.
The DPO, process owners and staff must agree the controls, which is often harder than the engineering.
The usual objection is “AI is too risky for a regulated business.” Unmanaged AI use is already happening in public tools. A controlled programme, with approved tools, measured accuracy and a log, reduces that risk.
Frequently Asked Questions
Will AI work with our existing systems?
Yes, in most cases. The AI connects to your CRM, case management or line-of-business system through its API or middleware, so staff keep working in the screens they know. If the system cannot be reached at all, see CRM and ERP integration.
Do we need a DPIA before an AI pilot?
Usually, yes. The ICO lists AI as innovative technology that needs a data protection impact assessment (DPIA) when combined with another risk factor. Phase 3 gives your DPO the findings to complete it before the pilot touches live work.
Will AI make decisions about our customers?
No. Wherever a Thornacre AI solution affects a person, staff approve each output before it takes effect. AI reads, classifies, forecasts and drafts; people decide. That keeps decisions outside the UK GDPR rules for solely automated significant decisions, and each approval is logged.
How do you stop our data leaking into public AI models?
Every AI tool runs on a controlled deployment that your CISO approves, not a public chatbot. Data sent to a model is limited to what each step needs, access follows your existing roles, and every call is logged. The AI policy names the approved tools, and phase 3 records where data goes, so the CISO and DPO can sign it off.
How do we start an AI transformation programme?
Start with a use case workshop. Score AI ideas from each team on value, risk and data readiness, with your DPO and CISO in the room. You leave with a ranked portfolio and one first use case to act on, with or without Thornacre.
If the board wants an AI plan and your DPO wants evidence first, book an AI use case workshop with Thornacre. Email hello@thornacre.com to arrange it.
This page is general guidance only; consult your legal or compliance teams for your specific requirements.