Operating Model Transformation That Fixes Processes, Roles and Data Ownership Before New Systems Land
When a mandate for change lands, the way work is organised has to change before any new system will help. We redesign processes, roles, governance and data ownership with your teams, so the change lasts after we leave.
The board has set a target to change how the organisation runs, and the COO must deliver it without disrupting customers or front-line teams. Operating model transformation is how Thornacre helps regulated organisations redesign the processes, roles, governance and data ownership behind their services, so change sticks and new systems have firm ground to land on.
| Area | Detail |
|---|---|
| Who it is for | COOs, CTOs and IT Directors, Heads of Data, CISOs, and Compliance Leads and DPOs in any regulated organisation |
| The problem it solves | Change programmes and new systems that stall because processes, roles and data ownership were never designed across teams |
| What we deliver | Process maps, a redesigned way of working, a data ownership model, data governance standards and trained teams |
| How we work | Working beside your staff, starting with discovery as the GDS Service Manual describes, then changing in small, tested steps |
| Regulations and standards | UK GDPR accountability, NCSC Cyber Assessment Framework governance, plus sector rules (see below) |
What problem does operating model transformation solve?
Operating model transformation closes the gap between what an organisation has decided to do and how its work is organised, owned and run. An operating model is the way an organisation arranges its processes, people, governance and data to deliver its services. When the model is unclear, each new system or restructure inherits the mess.
The trigger is often a deadline set from above, such as a board mandate, a regulator’s review or a merger, while the internal team is full with day-to-day work. So the work goes to contractors, and their knowledge leaves with them.
Each senior role sees a different symptom:
- COO: handoffs between teams that nobody designed, with staff rekeying data to bridge them.
- CTO or IT Director: a new platform that inherits the old workarounds, so the go-live date arrives but the benefits do not.
- Head of Data: board reports that disagree, because no one is accountable for each dataset.
- CISO: access decisions with no owner to approve them, and copies of data spreading between tools.
- Compliance Lead or DPO: no way to show who is responsible for personal data when an auditor asks.
Ownership is thin even at the top. The UK government’s Cyber Security Breaches Survey 2025 found that 27% of businesses had a board member responsible for cyber security, down from 38% in 2021. Among large businesses the figure was 66%.
Why is this not the fault of the people running services?
The root cause is structural. Most organisations grew around functions, product lines and old systems, not around the whole service a customer receives. Nobody designed the handoffs; they built up over years.
Data ownership is the sharpest case. Teams guard their data because they carry the risk, and nobody owns the shared view. Internal politics add friction: finance wants results this year, business leads protect headcount, and the board judges IT on a go-live date.
Waiting makes it worse. Each year of contractor-led change without skills transfer leaves the next programme more dependent on outside help.
How does Thornacre deliver operating model transformation?
Thornacre delivers operating model transformation in 6 phases, from inside your teams to a handover your own staff can run. The diagram shows the order, with the point where you agree or escalate data ownership.
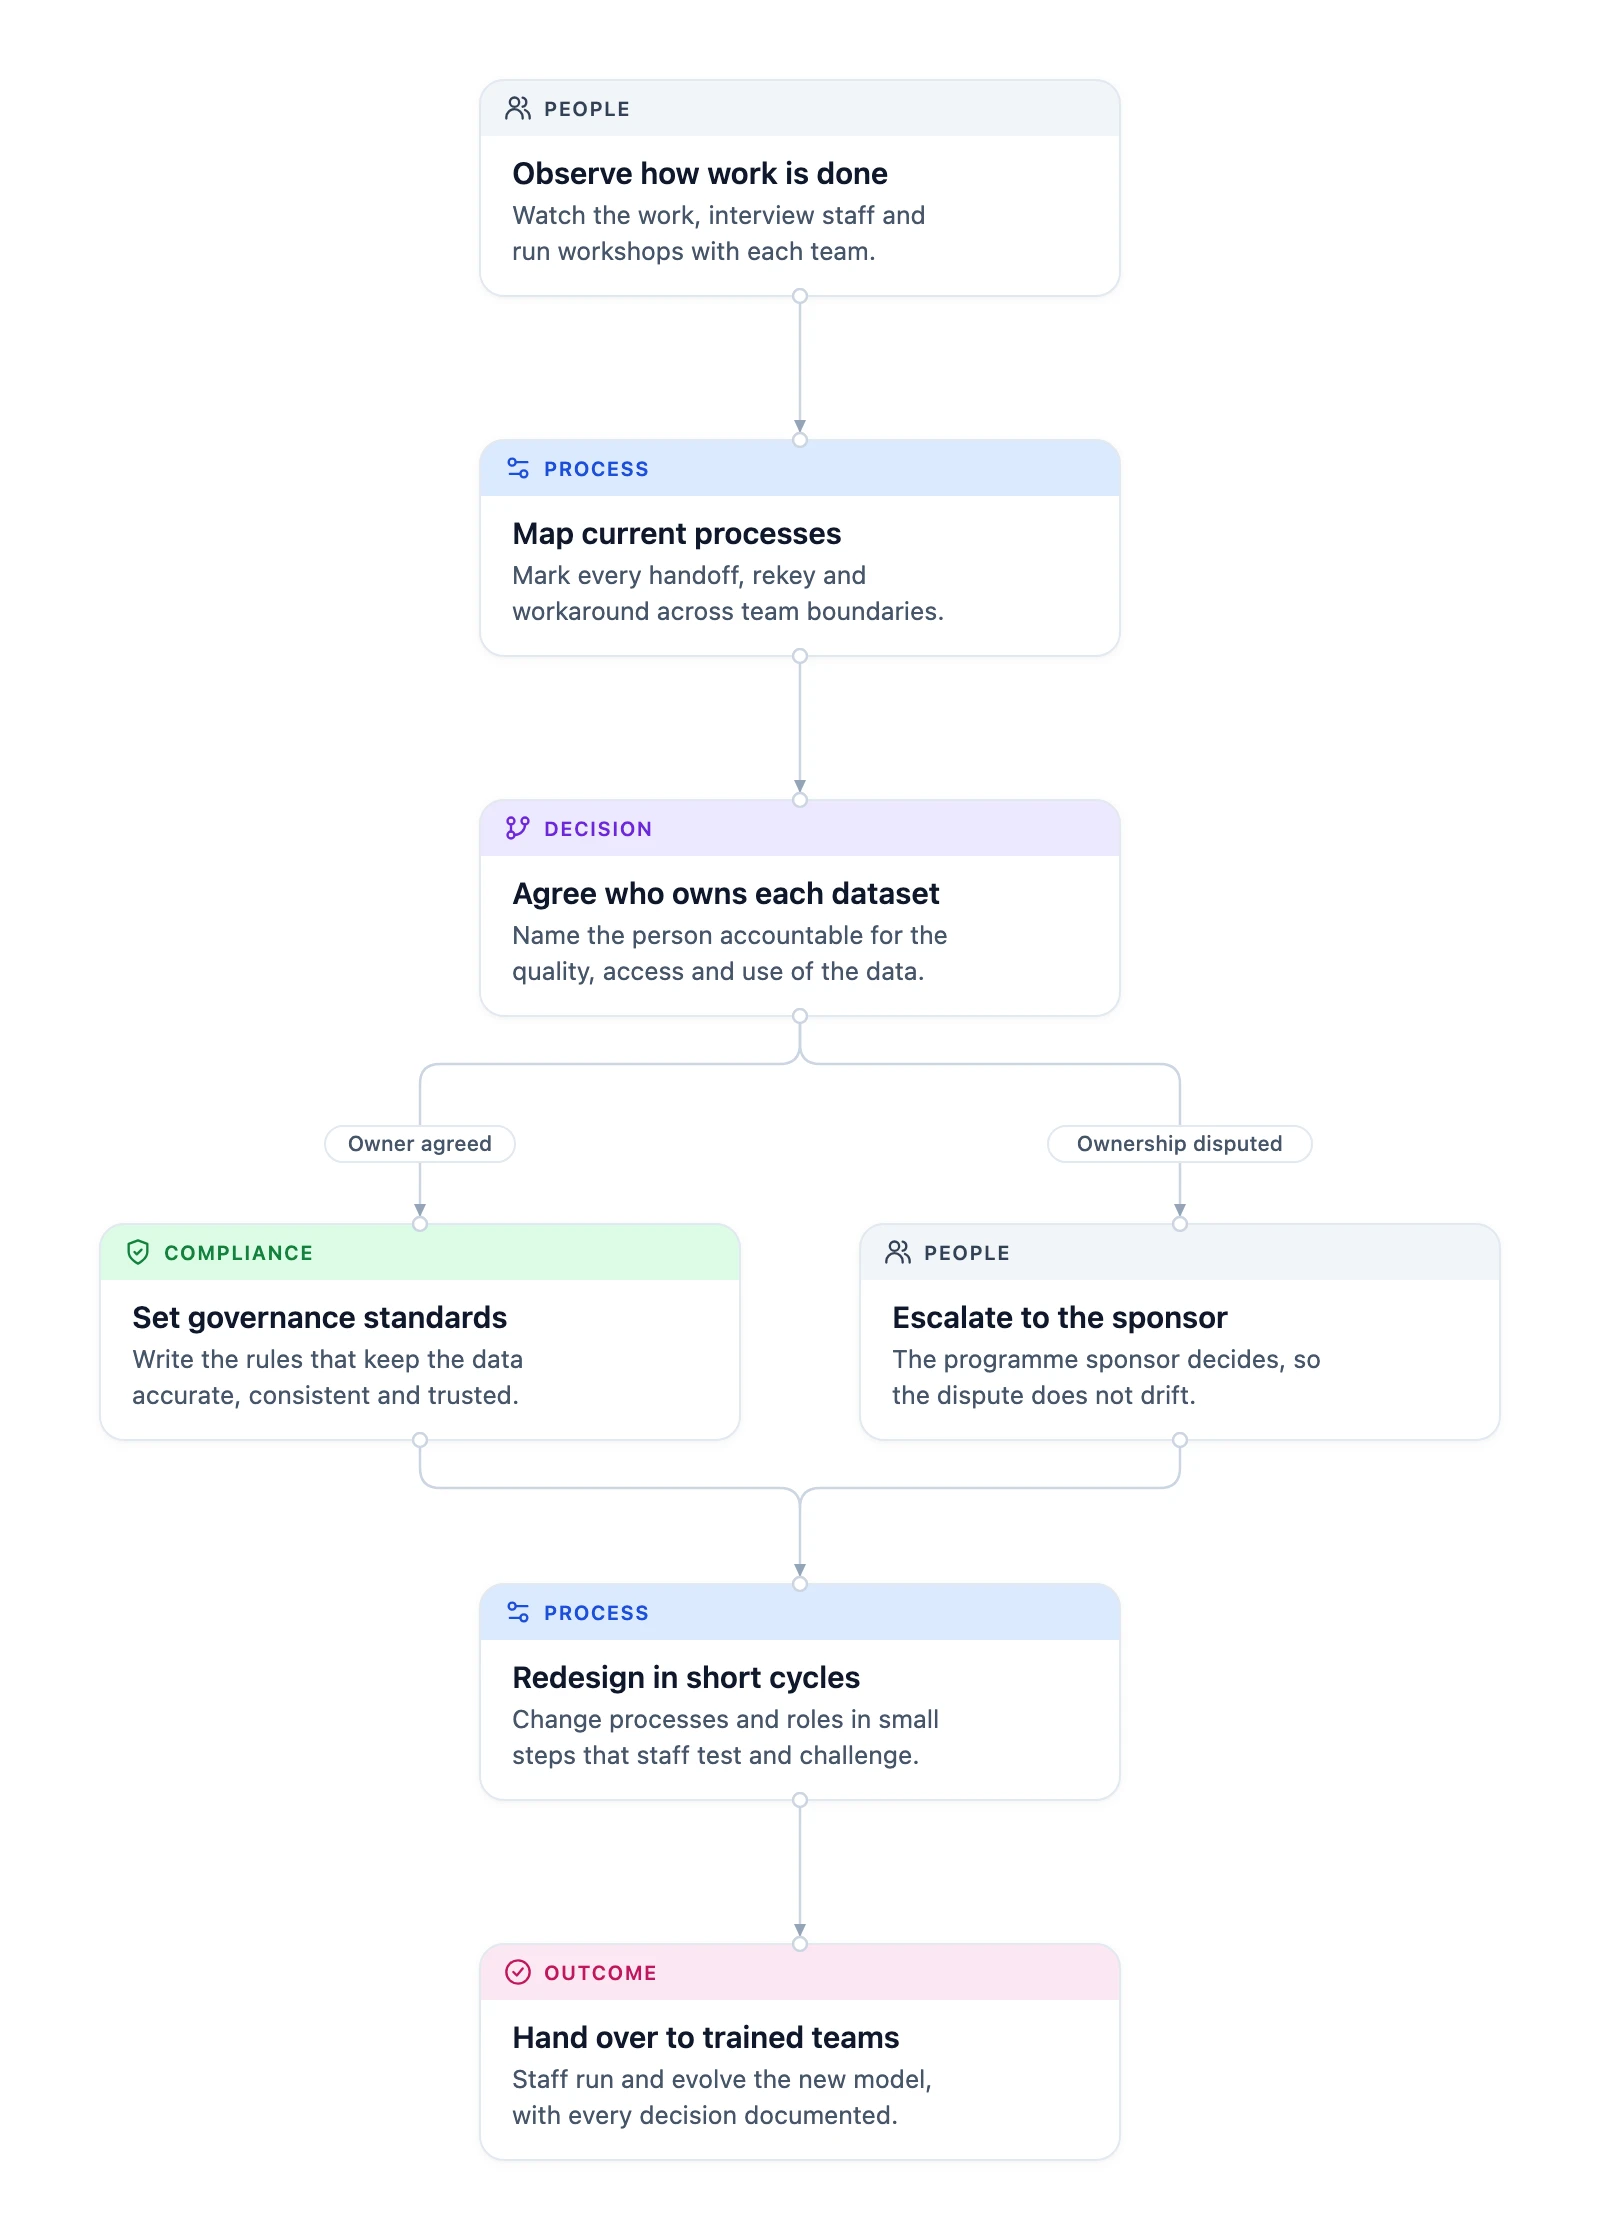
- Observe how work is really done. We sit with your teams, watch the work, run interviews and hold workshops. Outcome: evidence that staff recognise as their own week.
- Map current processes end to end. We map each process across team lines, marking handoffs, rekeying and workarounds. Outcome: one shared picture of where time is lost.
- Agree who owns each dataset. A data owner is the named person accountable for the quality, access and use of one dataset. Outcome: a list of owners, with disputes in plain sight.
- Set governance standards, or escalate. Where ownership is agreed, we write the standards that keep data accurate and consistent. Where it is disputed, the programme sponsor decides, so the question does not drift.
- Redesign in short cycles. We change processes and roles in small steps that staff test and challenge. Outcome: progress you can see early.
- Train and document throughout. Training runs during the project, not just at the end, and we write down every decision. Outcome: your teams run the model without us.
The insight behind this order: a new system inherits the operating model it is dropped into, so if nobody owns the data, the new platform will be as unreliable as the old one.
You can test this yourself this week. List the 10 datasets your services use most, and write beside each the name of the person accountable for it. Each blank or dispute marks a place where your change will stall.
What do you get from an operating model transformation?
You keep the artefacts and the skills, not just a report, because each item is built with your staff.
| Deliverable | What it gives you |
|---|---|
| Process maps | An agreed record of how work flows today, with handoffs marked |
| Data ownership model | A named owner for each key dataset, with escalation rules |
| Data governance standards | The rules that keep data accurate, consistent and access-controlled |
| Requirements | Structured requirements for complex, multi-team programmes |
| Trained teams | Staff who can manage and evolve the new ways of working |
| Decision log | A plain record of every decision and who made it |
Which regulations does operating model transformation help you meet?
Operating model transformation gives every regulated organisation evidence of accountability: named owners, written governance and mapped processes. Two cross-sector frameworks set the baseline.
- UK GDPR accountability: the Information Commissioner’s Office (ICO) Accountability Framework asks organisations to take responsibility for personal data and show how they comply.
- Security governance: Principle A1 of the NCSC Cyber Assessment Framework (CAF) expects “appropriate management policies, processes and procedures in place to govern” the security of network and information systems.
Each sector adds its own expectation of clear ownership, and the same ownership model supports each.
| Sector | Regulation or framework | What it requires | How the service addresses it |
|---|---|---|---|
| Banking and payments | FCA operational resilience, SYSC 15A | Identify and document the people, processes, technology and information behind each important business service | End-to-end process maps with named owners for each service |
| Insurance | FCA Consumer Duty, PRIN 2A.9 | Monitor and evidence the outcomes customers receive | Owned datasets and quality rules behind outcome reporting |
| Private healthcare | Data Security and Protection Toolkit (DSPT) | Self-assessment against the National Data Guardian’s 10 data security standards | Named data roles and written governance as evidence |
| Energy, water and critical infrastructure | NIS Regulations 2018, assessed with the CAF | Governance of the security of essential services | Clear roles across operations, IT and security |
| Public sector | GovS 005 Digital | Expectations for managing digital, data and technology | Clear roles across business and IT |
The GDS Service Standard sums up the design principle in its second point: “Solve a whole problem for users.”
Should you redesign the operating model or buy a new system first?
Redesign the operating model first when the problem sits between teams; buy a system first when one team owns a clearly failing tool.
| If this describes you | Start with | Why |
|---|---|---|
| Teams dispute who owns key data | Operating model transformation | No system can settle an ownership dispute |
| Staff rekey data between teams | Process redesign, then integration | Fixing the handoff shrinks what you build |
| One system is out of support, but the process works | System replacement | The model is sound; the tool is not |
| A board deadline and no spare capacity | Both, with skills transfer in the contract | Avoids repeat contractor dependency |
If your priority is the platform and data delivery, see Thornacre’s digital transformation service. For reporting and data platforms, see data analytics and AI.
When is operating model transformation not the right choice?
Operating model transformation is the wrong choice when the problem is one failing system with clear owners, or when no senior sponsor will make decisions. In the first case, a migration is the simpler route. In the second, you get maps that nobody acts on.
The approach also asks for staff time for interviews, workshops and testing, so plan it alongside day-to-day work.
The common objection is: “We will lose control and knowledge to a supplier.” Thornacre answers it in 3 ways. Your staff work in every phase, not just at handover. Training runs during delivery, not at the end. We write down every decision, so your staff can explain and change it without us.
Frequently Asked Questions
How much of the organisation should be in scope?
Scope should start with the services where handoffs and data disputes block a known priority, such as a redesign the board has asked for. Discovery on 1 service tests the approach and builds evidence. Wider change follows only where that evidence shows the same problems repeat across teams.
Does this work with the systems we already run?
Operating model transformation works with your existing CRM, finance and line-of-business systems, because it changes how work and data ownership are organised around them. Process maps show where systems force rekeying or workarounds. Some fixes need no new technology; others become scoped requirements for integration or replacement.
Will the change disrupt customers or front-line teams?
The risk of disruption stays low because processes change in small, tested steps, not in one cutover. Staff try each change before it becomes standard, and the old way stays in place until the new one works. Front-line teams help design each change.
How does a data ownership model help with audits?
A data ownership model gives auditors and regulators a named person for each dataset, with written rules for quality and access. That is the accountability evidence the ICO Accountability Framework asks for, and the same record supports the sector reviews in the regulations table above.
Will we depend on Thornacre after the programme ends?
Thornacre plans its own exit from the start. Training runs throughout, we record every decision in plain English, and your staff take part in each phase. By handover, your teams can run and evolve the new ways of working without outside help.
How do we start an operating model transformation?
Start by naming a senior sponsor who can settle ownership disputes, then pick 1 service with a known problem. The first phase is discovery: observation, interviews and process mapping in that service. That gives you evidence for the business case before you commit to wider change.
If a board mandate is forcing change and you are not sure where the handoffs break, ask us for an operating model assessment workshop. Email hello@thornacre.com and we will agree a short discovery on 1 service to start.
This page is general guidance only; consult your legal or compliance team for advice on your specific obligations.